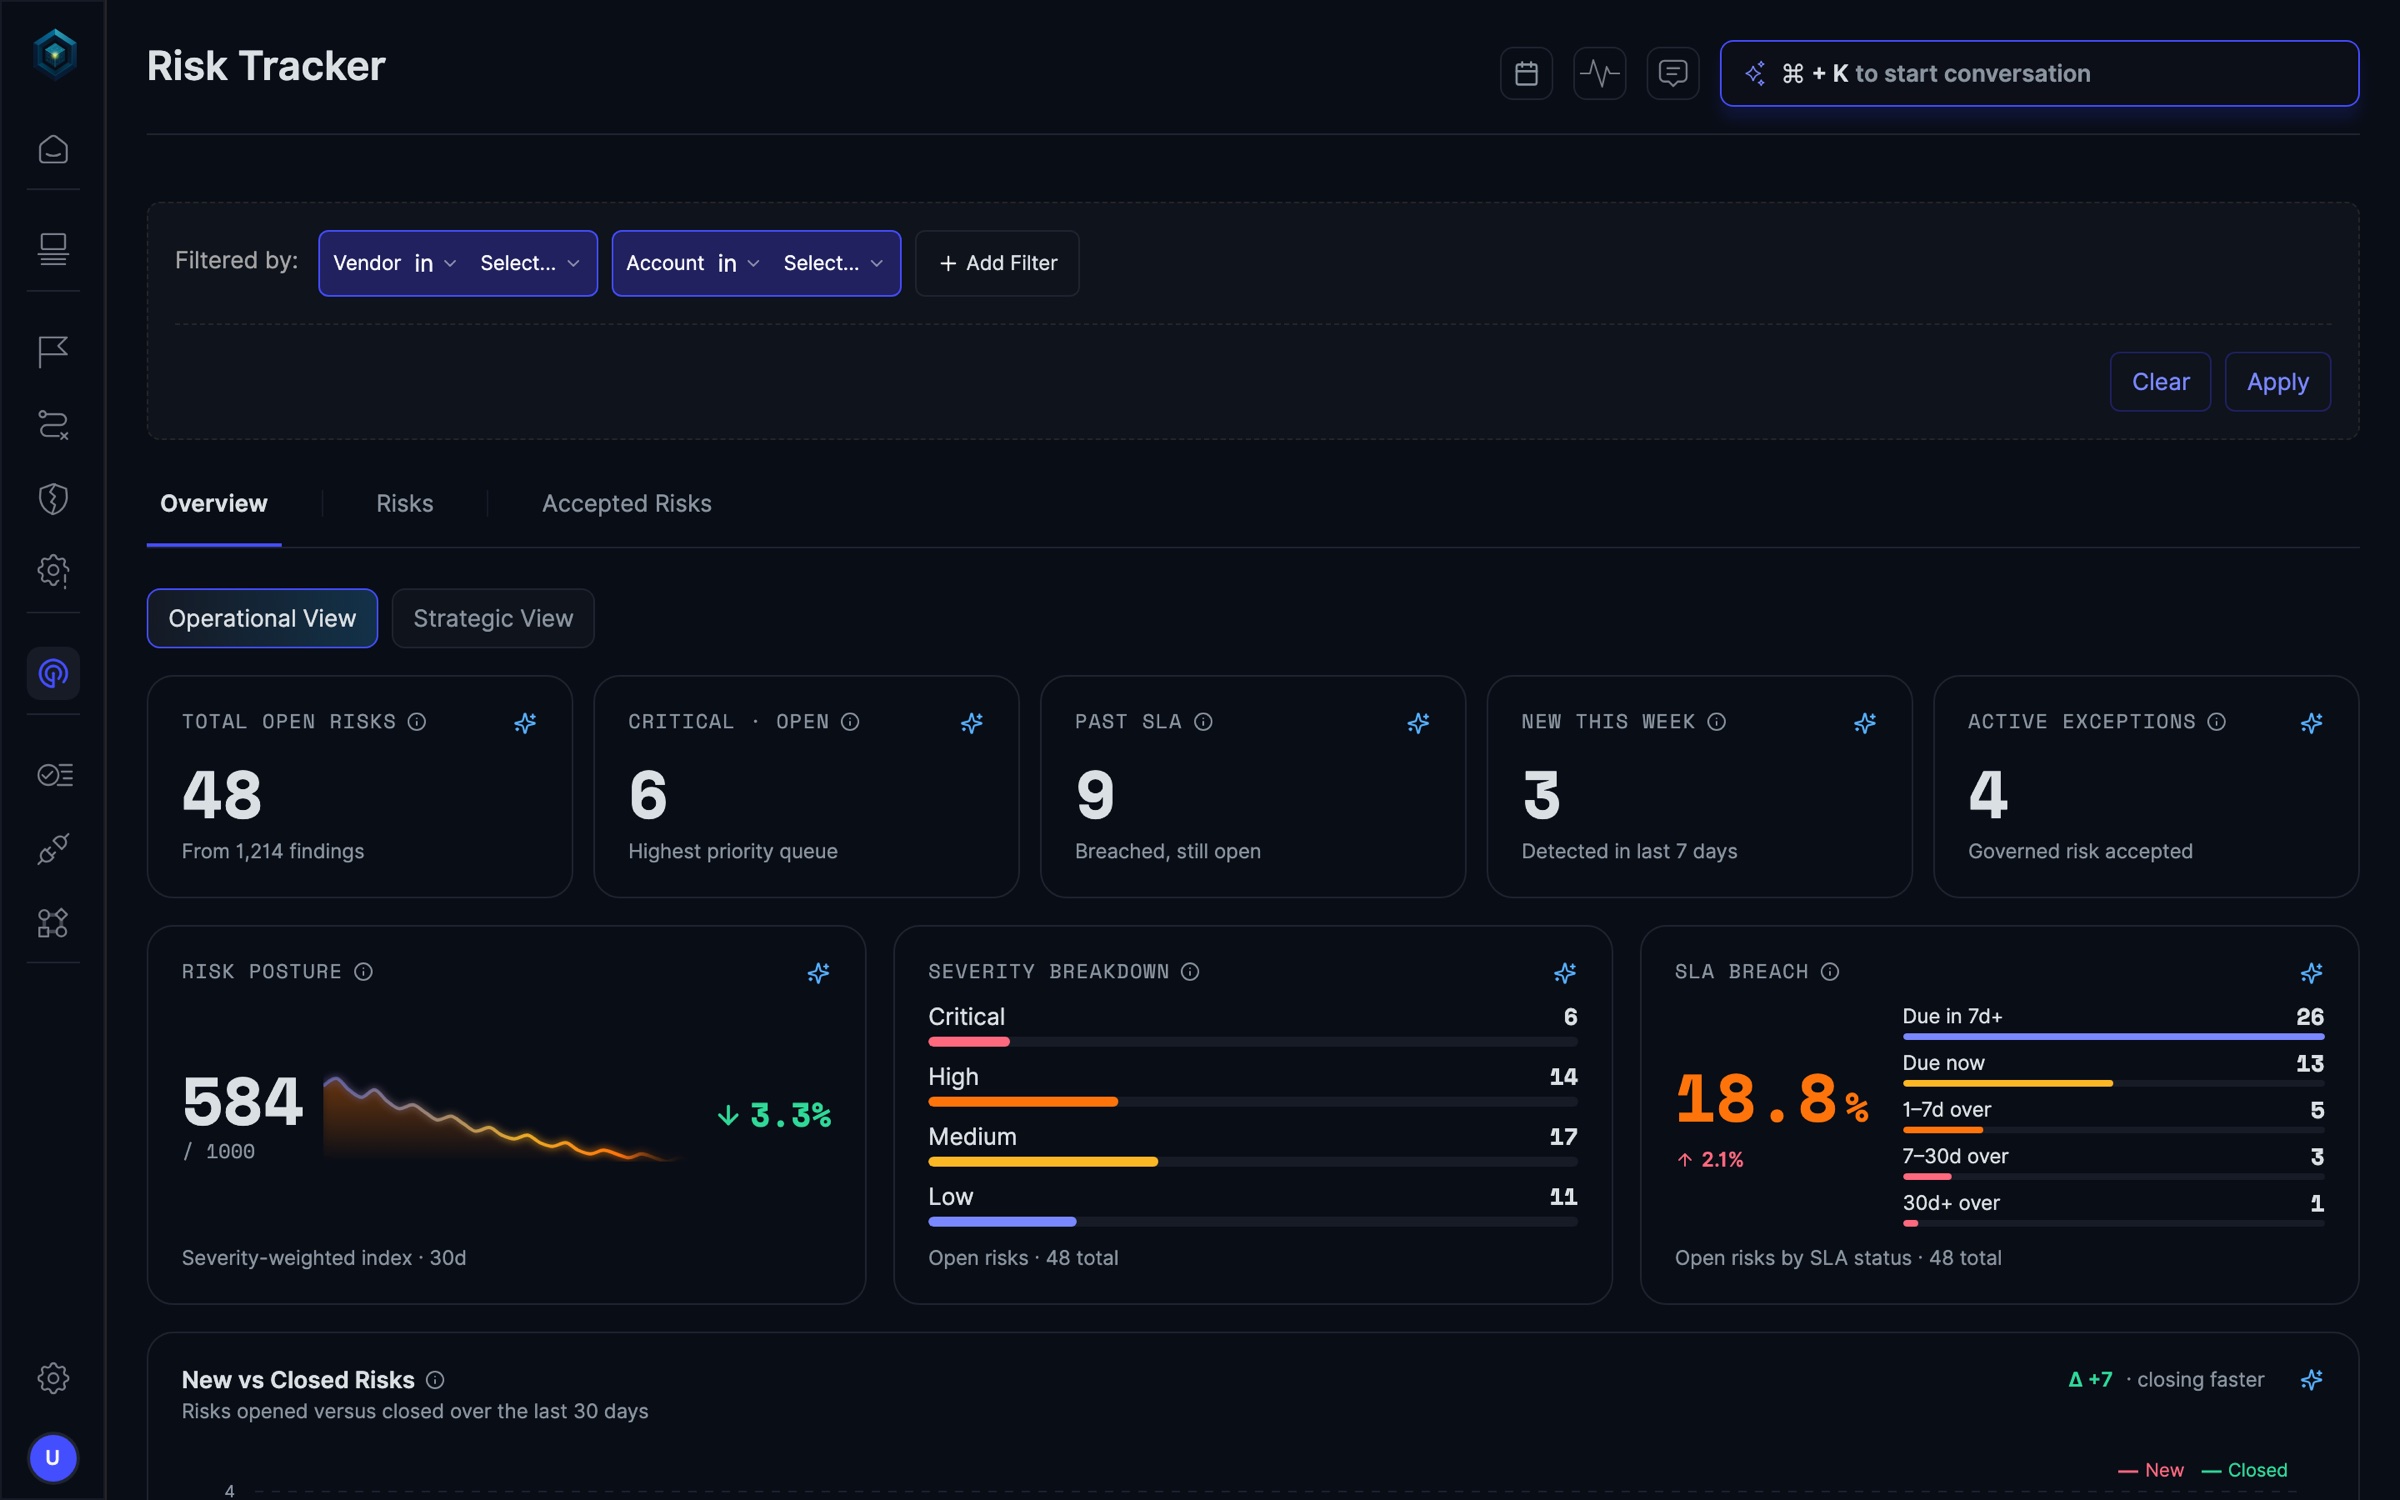
I designed a faster list when the team needed a risk model.
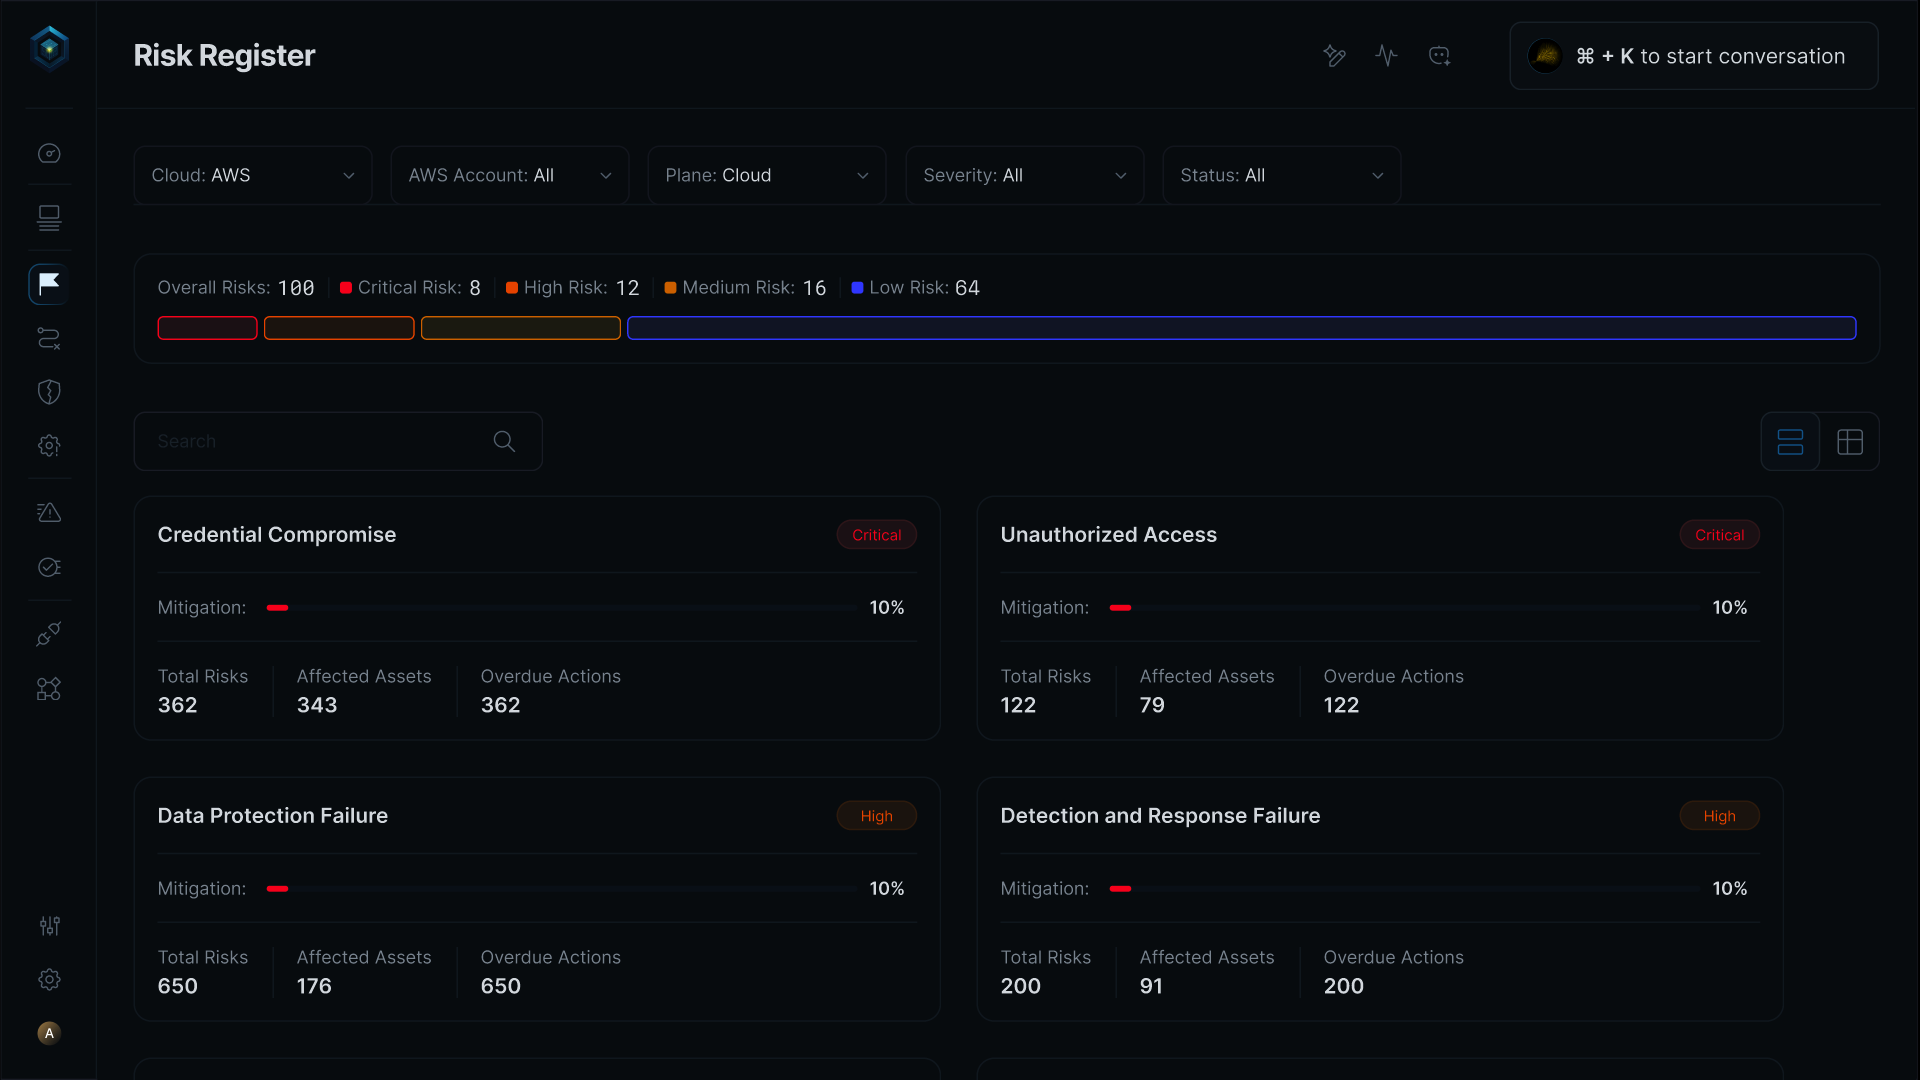
My v1 was finding-centric. It had Active / All tabs and every CVE and misconfiguration was its own row, so it was a cleaner, quicker queue. I took it almost to staging before our security SME stopped it and sat me down to show me how risk actually works.
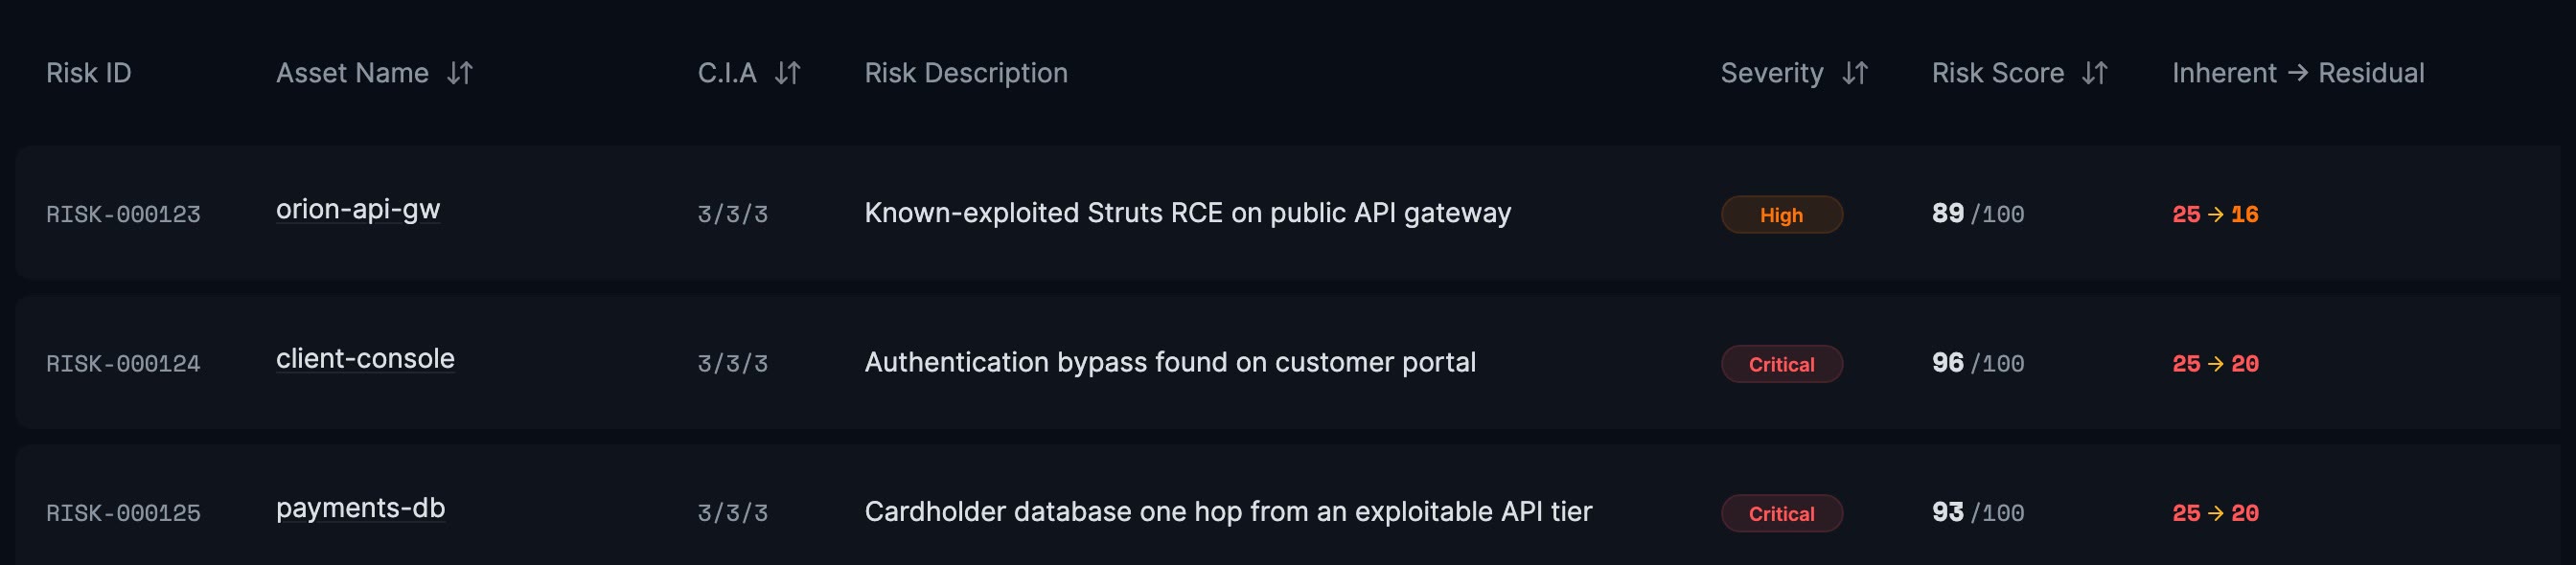
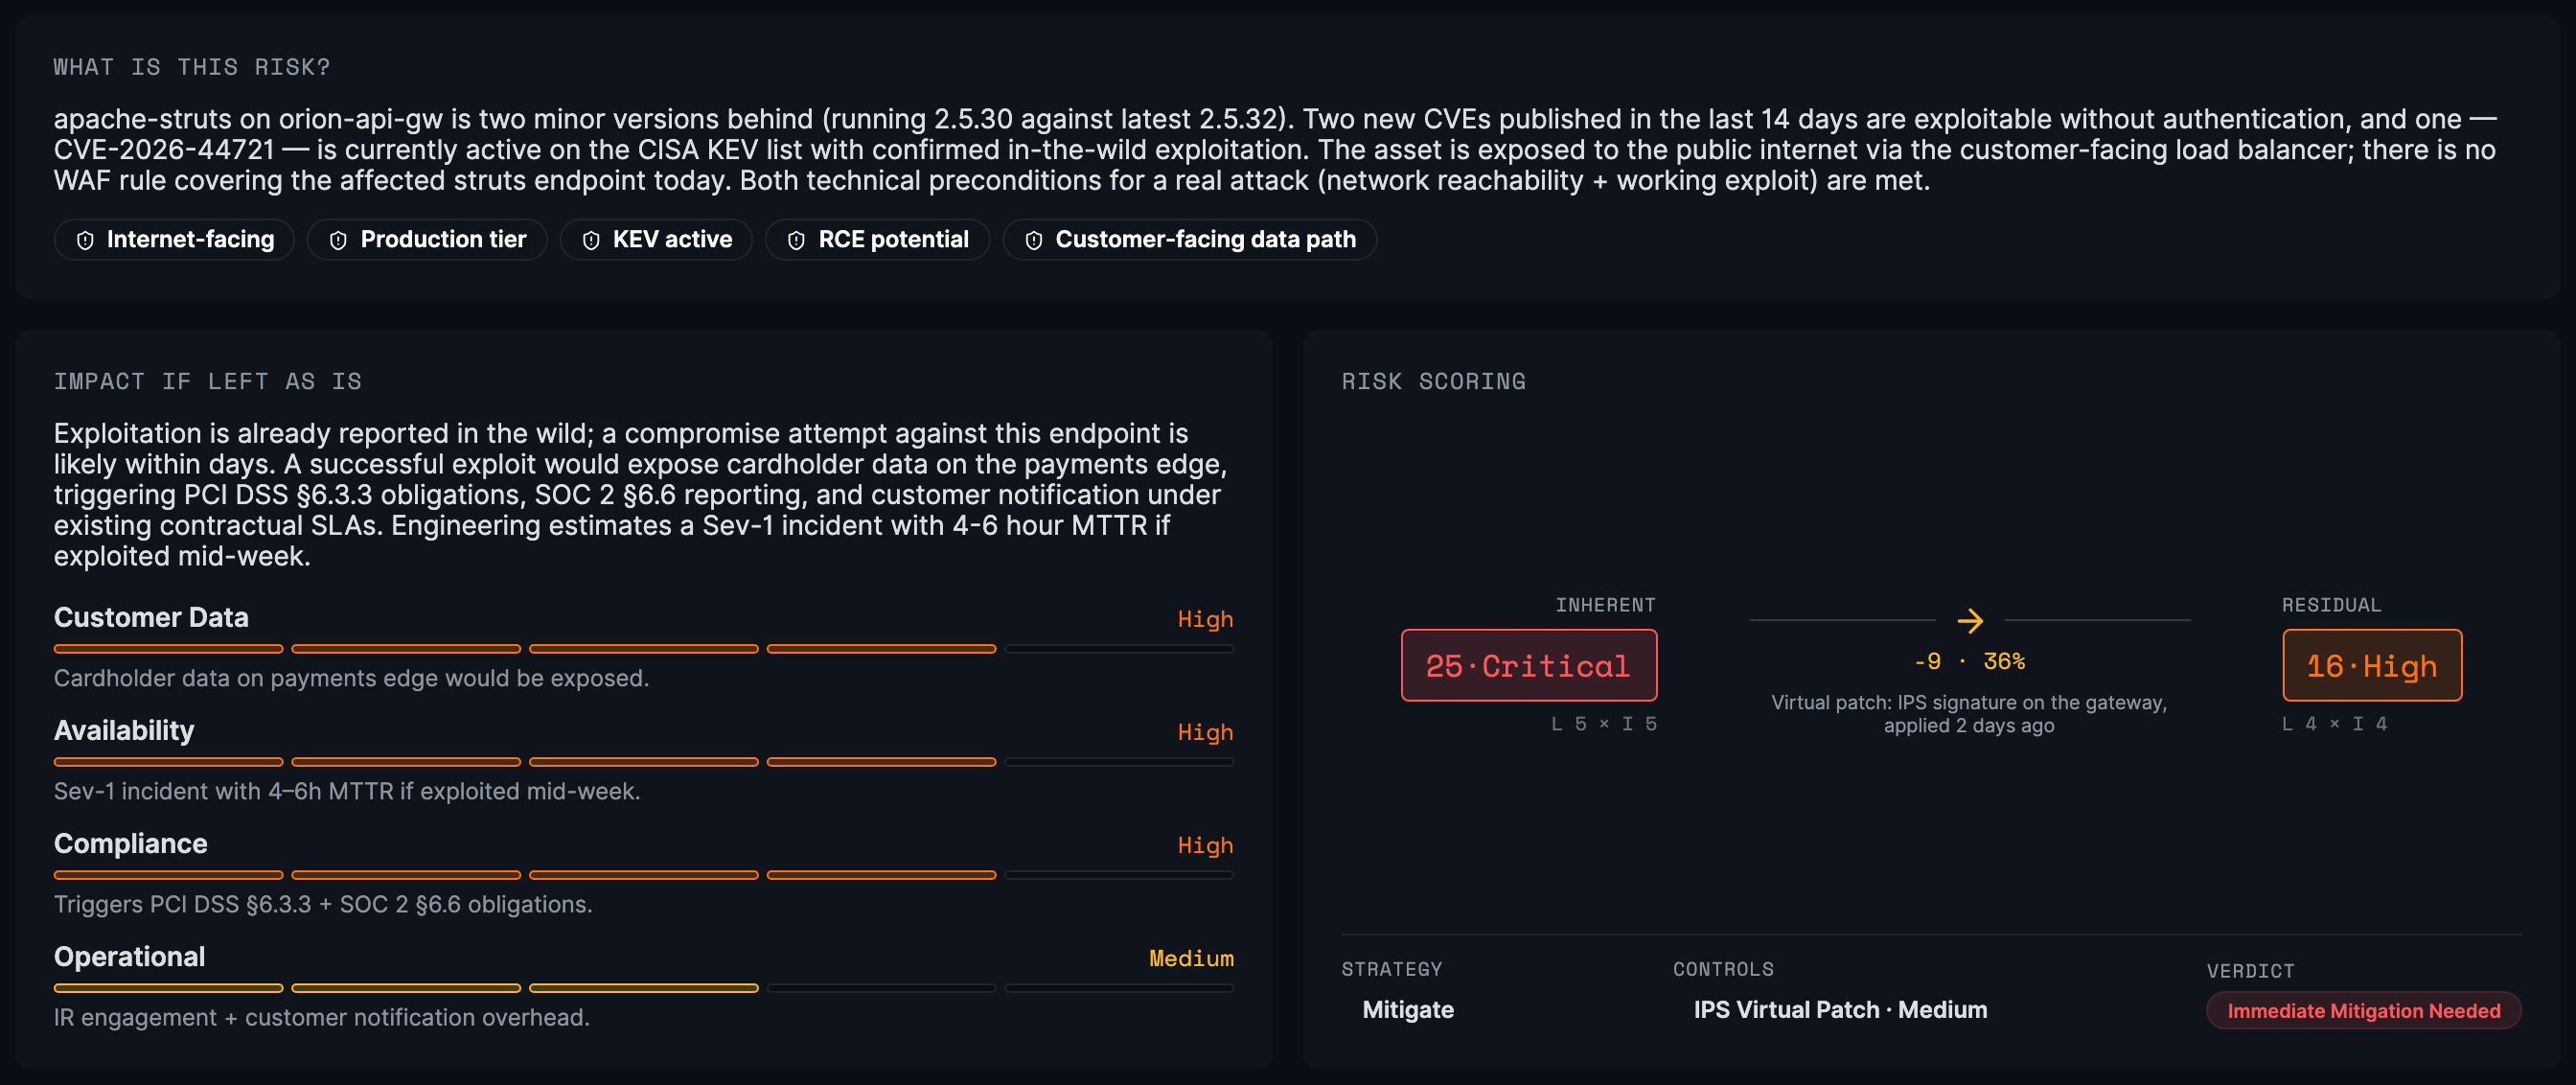
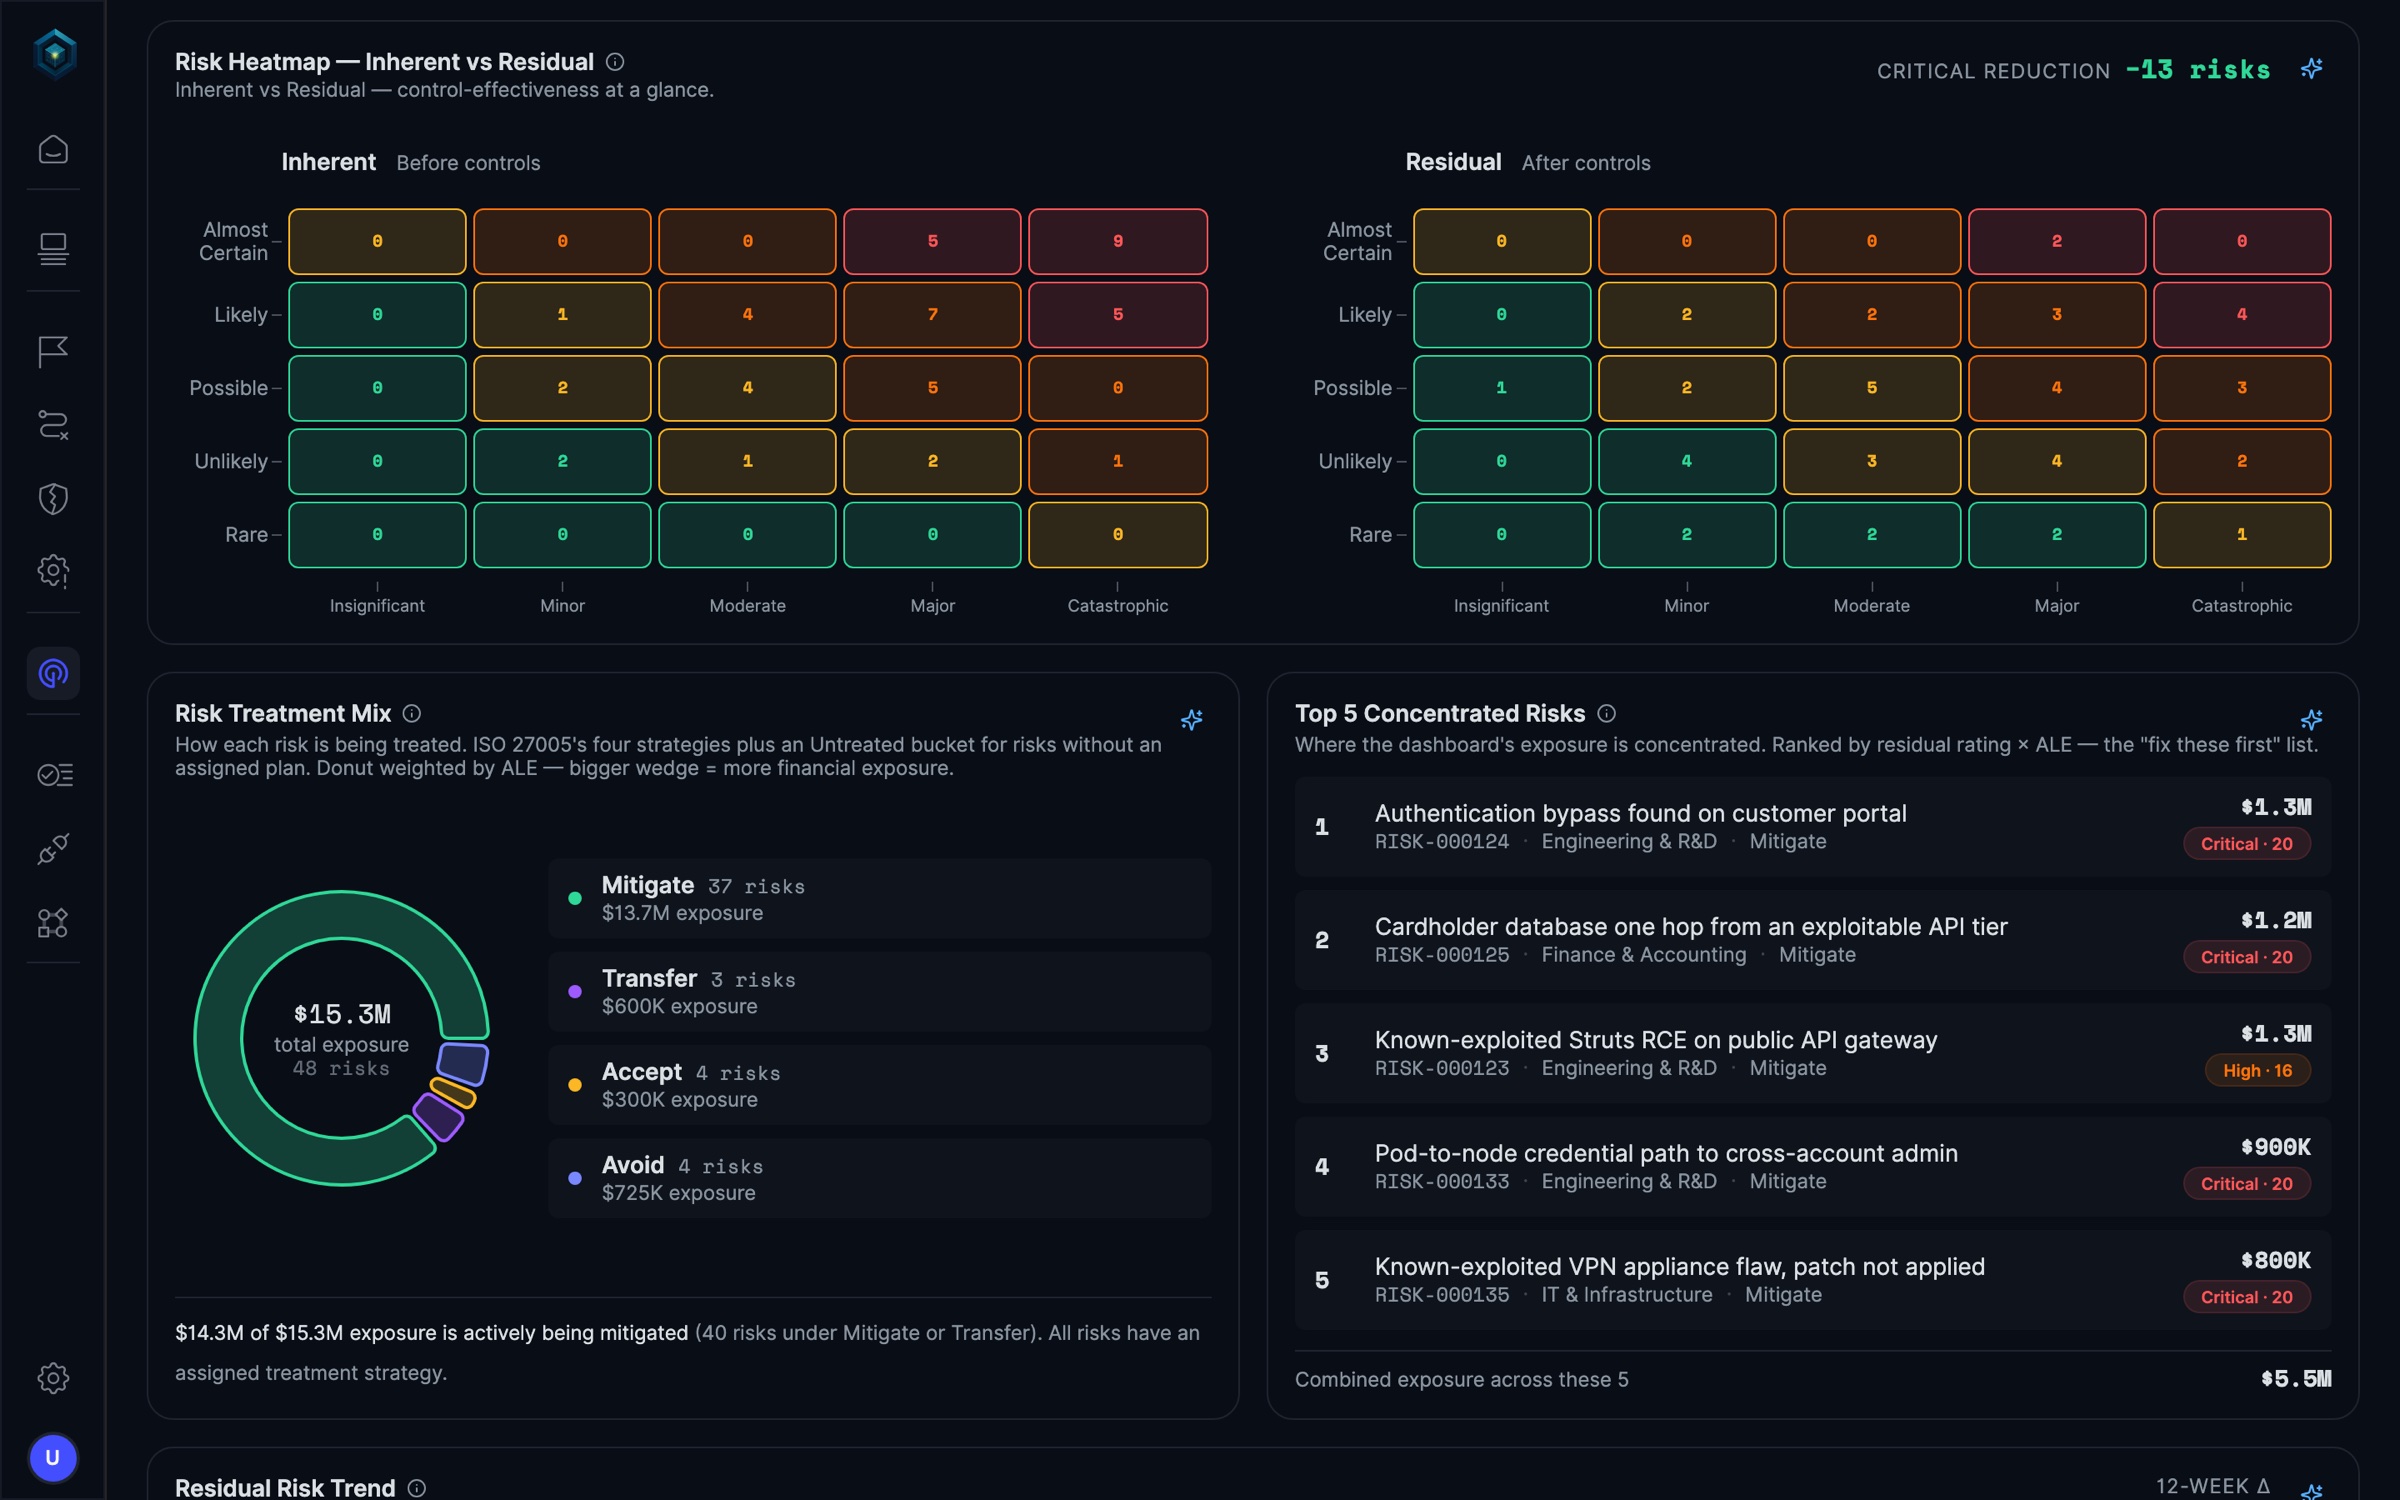
A finding isn't a risk, he said. An asset carries risk, and findings are evidence that adds to it. He showed me the register his team really uses, an ISO 27001-style register with 34 columns, inherent and residual scoring and defined treatment strategies. I'd optimized the wrong thing, so I threw out the finding-centric IA and started again from the asset.
That changed how I work. When a domain expert owns the mental model, I design to their model instead of swapping in a tidier one of my own.